18/11/2026
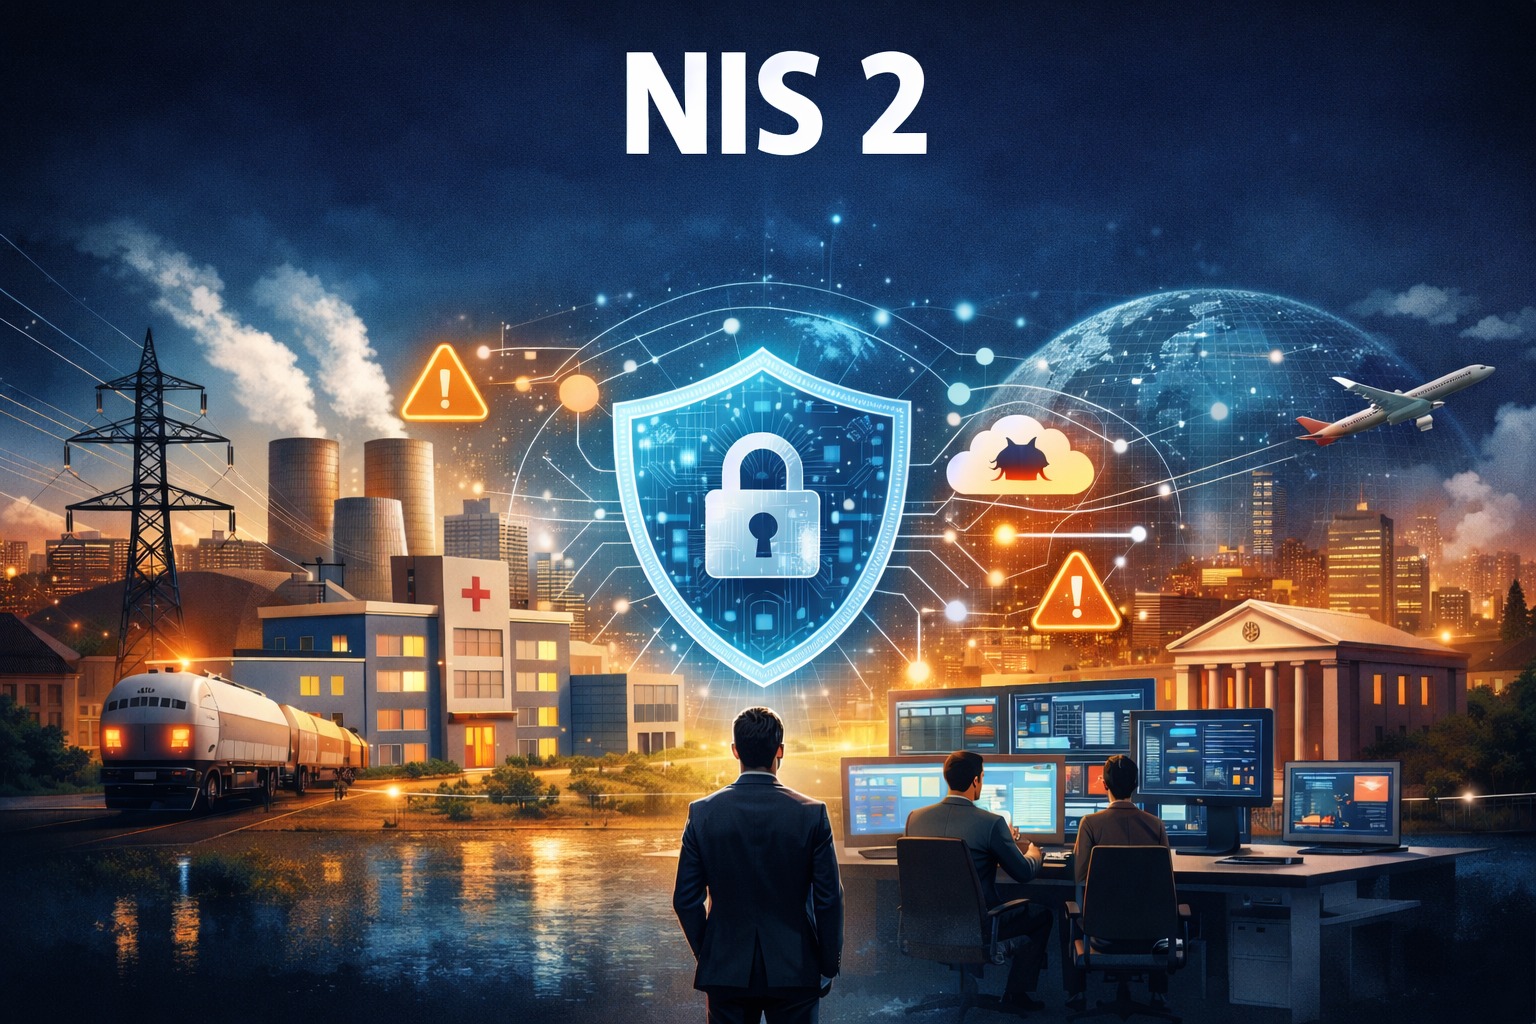
The adoption of the NIS 2 Directive marks a profound change in the way the European Union approaches cybersecurity. Whereas earlier legislation was oriented primarily towards formal compliance, the new framework focuses on a far more pragmatic reality: the actual capacity of entities to withstand, operate and adapt in the face of cyber incidents. In this context, security can no longer be treated as an ancillary function; it becomes a central element of how an organisation operates, with a direct impact on business continuity and public trust.
In a digital ecosystem in which infrastructures are interconnected and interdependent, the vulnerability of a single entity can trigger cascading effects with systemic impact, affecting not only the operator concerned but also its partners, its suppliers or even entire sectors of activity. For this reason, NIS 2 considerably broadens the range of organisations within its scope, covering not only traditional operators of essential services but also entities in fields such as healthcare, energy, transport, public administration and digital infrastructure. This extension reflects an undeniable reality: cybersecurity is no longer a sectoral issue but a matter of general interest, bound up with the functioning of society as a whole.
The central concept of the Directive is resilience, understood not as a mere technical capability but as a complex organisational function that must be embedded at every level of decision-making. Resilience means more than protection; it involves anticipation, response and continuous adaptation. A resilient entity is one that knows its vulnerabilities, constantly assesses its risks and adjusts its internal mechanisms to cope with threats that are constantly evolving. In this sense, resilience becomes a dynamic process, not a static objective.
In practical terms, this requires the development of internal mechanisms that allow incidents to be identified early, their impact to be contained and essential activities to be resumed quickly. It is not only a matter of technology, but also of processes, clearly defined responsibilities and an organisational culture geared towards prevention. Without these elements, even the most advanced technical solutions may prove ineffective.
To that end, the Directive requires an integrated approach to risk management. Implementing disparate technical solutions or reactive measures is no longer sufficient. What is needed is a coherent architecture comprising internal policies, clear procedures, monitoring mechanisms and continuity plans. Crucially, security becomes part of day-to-day operational processes rather than an additional layer applied after the fact.
Along the same lines, the drafting of internal instruments and specific procedures tailored to each organisation, together with the effective and verifiable implementation of the measures adopted within companies or public institutions, is essential to achieving a genuine level of compliance and resilience. The mere existence of documents is not enough; they must be known, applied and periodically tested in practice.
A particularly significant element is the accountability of management bodies. NIS 2 expressly places responsibility for cybersecurity at management level, which brings about a change of perspective: security is no longer solely a technical issue but one of governance and strategic ownership. Management must understand the risks, allocate adequate resources, set priorities and exercise genuine oversight of how the measures are implemented. This responsibility also entails the need for ongoing training of decision-makers, so that they are able to take informed decisions in a field characterised by technical complexity.
The Directive also introduces strict incident reporting obligations, with short deadlines and clear requirements as to the content of notifications. This mechanism is not merely a formality; it contributes to the creation of a European early-warning system, facilitating information sharing and a coordinated response among Member States and institutions. In this way, every reported incident becomes a source of learning for the entire ecosystem.
Nevertheless, the real challenge lies not in ticking off the legal requirements but in turning them into a genuine and sustainable organisational practice. Implementing NIS 2 requires cultural change, investment in technology and human resources, and the development of solid in-house expertise. For many entities, especially those with a low level of security maturity, this process may be difficult, but it is unavoidable. Without a serious approach, the risks do not disappear; they grow.
In reality, the Directive does no more than formalise a need that already existed. Cyber threats are not hypothetical but real and increasingly sophisticated, and their impact can be severe, in financial, reputational and operational terms alike. In this context, resilience becomes a condition of operational survival, not merely a theoretical concept.
Organisations that treat these requirements as a mere bureaucratic obligation risk remaining vulnerable and exposed, whereas those that integrate them strategically into the way they operate strengthen their capacity to respond, protect their business and enhance their credibility with partners and beneficiaries.
Consequently, the NIS 2 Directive should not be seen as a set of rules imposed from outside, but as a framework that provides the direction needed to build organisations capable of operating in an uncertain and dynamic digital environment. Resilience is no longer a competitive advantage but a fundamental requirement, and the capacity to adapt will make the difference between organisations that endure and those that are overtaken by today's realities.
Author: P.A.
Copyright © 2026. All rights reserved.
We use cookies that are strictly necessary for the website to work and, only with your consent, statistics cookies (Google Analytics) that show us how the website is used. You can change your choice at any time under “Cookie settings”.
